Friday, September 6, 2013

How to remove PUP.Optional.Tarma.A


Description of PUP.Optional.Tarma.A

PUP.Optional.Tarma.A can be categorized as a Trojan horse that belongs to the family group of PUP. Optional. So far as to now, we have found two of its siblings-- PUP.Optional.InstallCore.A, PUP.Optional.BrowserProtect.A.  PUP.Optional.Tarma.A can get on your computer without your permission and your computer will be in big trouble if no proper measures are taken to cope with it.
 
If your computer is infected with PUP.Optional.Tarma.A,  I am sure that you should remove it as soon as possible as I state its horrible threats that come along with it successful installation in your computer. As a Trojan horse, its priority is to help crackers to compromise your computer and then get control of it. PUP.Optional.Tarma.A can open backdoors – some ports--to make crackers easier to sneak into your computer. Once successfully infiltrated, those cyber criminals can monitor everything you do on your computer; they can record your keyboard activity and your private information like online bank account or other important accounts. Besides, PUP.Optional.Tarma.A can bring other serious threats, such as News.net, NSA Internet Surveillance Program Virus, Trojan Horse Generic33.CDPK and other powerful viruses and to crown the whole, it must have modified registry and system setting to make it illegally stay in your computer.


How caught it

After learning how danger it is, you might want to keep it away from your computer and curious about how you get infected with this virus. There are various ways but we conclude them in three types: First, visiting insecure sites or download something like music, PDF files or movies free from those sites. Second, installing software by default way. Some programs are bundled with those viruses and if you uncheck it, you get it without a doubt. Third, which is terrible, is that other viruses have installed it, which means there are other viruses in your computer. But don’t panic , we will show you’re the way to remove it , and if you still cannot remove it completely, please click here to get professional help.


Removal Instruction

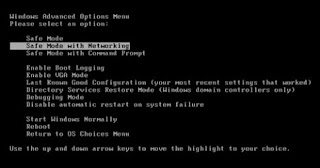
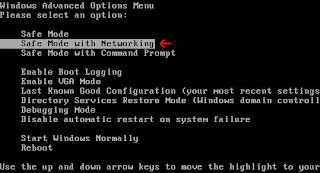
Step 1: Enter the Safe Mode with Networking.
    Keep tapping F8 when your computer restart and then choose Safe Mode with Networking.


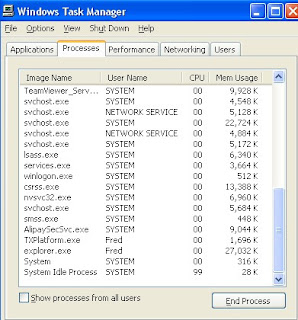
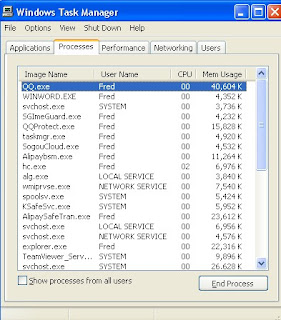
Step 2: enter the task manager and end process.
     Hit Ctrl+Alt+Del at the same time and click start task manager.
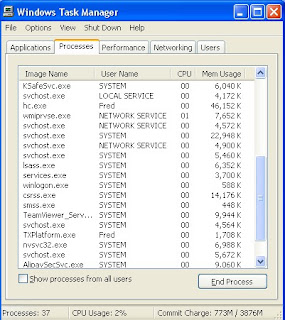
     Find the Ransdom.exe and end it

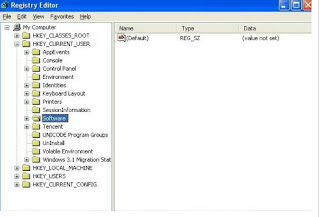
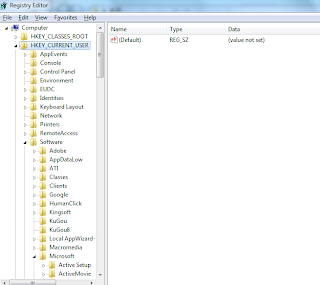
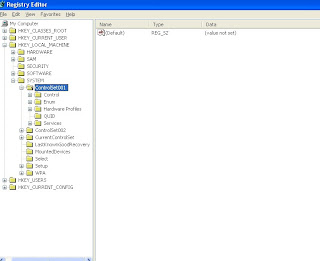
Step 3: Enter the registry editor.
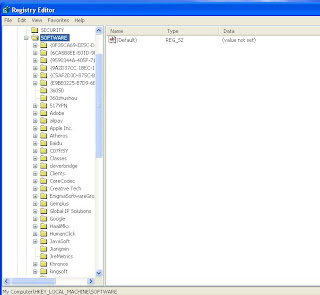
    Hit Win+R>>type regedit
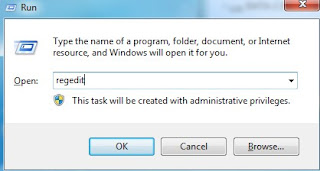


    Go to the following registry entries and delete them.
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ‘Random’
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe
 Step 4: Reboot the system to make your change effective.


Friendly advice: You should be more careful when dealing with registry editor. If you still could not remove it, please click here to get help.


Wednesday, September 4, 2013

Infected with Trojan Horse Generic34.PDW Virus! Remove it Now


What is the Trojan Horse Generic34.PDW Virus

Trojan Horse Generic34.PDW Virus can be categorized as a Trojan that belongs to the family of Trojan Horse Generics.   If your computer is infected with it, it is highly recommended that you should remove it immediately because this virus is a serious threat to your PC.

Under the help of other viruses or programs, this virus can get on your computer. Besides, you can also get your computer infected by the going to those insecure sites which contain virus or download programs from here. Most of that free softwares contain viruses.

If unluckily infected, that compromised computer will suffer a lot. First begins with the resources being taken up and severely slow down the performance, which make computer sometimes crash down or freeze.  And second is that its residence in your computer will open Pandora’s Box—bring so much dangerous threats to the computer, like PUP.Optional.Tarma.A, Trojan Horse Generic33.CDPK, Homeland Security Virus or browser defender, which any one of it will cause much damage to the computer. Third is its capacity to modify the system’s setting and add corrupted registry entries. That may explain why your home page is replaced by others or computer runs weird. In addition to those, Trojan Horse Generic34.PDW Virus can offer convenience to cyber crackers who can gain the access to the compromised computer and then monitor your every step or activity you move in your computer.  Your personal information will risk being exposed to others. It is a real danger. Removing it now.

In the following post, we will show you how to remove it and if you still cannot remove it, please feel free to contact professional online tech support.


Removal Instruction:

Step 1: Enter the Safe Mode with Networking.
    Keep tapping F8 when you restart your computer and then choose safe mode with networking.


Step 2: End the process
Press”Ctrl+Alt+Del” to enter the process and then end Random.exe

Random.exe


Step 3: enter the registry editor.
Press”Win+R” and then type “regedit”,hit Enter.


Find the following registry entries  and delete them:
 HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” = ‘0’
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Policies\Attachments “SaveZoneInformation” = ‘1’

Find the following files and delete them:
%APPDATA%\[RANDOM CHARACTERS].js
%APPDATA%\[RANDOM CHARACTERS].pad
%USERPROFILE%\Start Menu\Programs\StartUp\runctf.lnk

NOTE:  Dealing with registry should be more careful because any step wrong will lead system to failure. If you still could not remove it, please contact  tee support for professional online tech support.

Tuesday, September 3, 2013

Manually Remove FLV Player by Somoto Ltd


What is FLV Player by Somoto Ltd
FLV Player by Somoto Ltd can be categorized as an unwanted program that gets install in your computer without your permission. It can be distributed by spam emails, free downloads or contained in other webpages that it catches when you visit these sites. It is also bundled with other programs and if you choose quicker way to install the program, you are more likely to pick it up.

Once you get it, you will find that your browsing experience or normal work or entertainment in your computer is interfered by FLV Player by Somoto Ltd as it keeps popping up a message, asking you to install the program. If you install or update it, FLV Player by Somoto Ltd will install adware or other popup in your computer that also are major threats to your computer. When it successfully installed in your computer, it can bring other devastating threats like webcake, delta search.com or Trojan Generic or above all, the most notorious FBI ransomware. In addition to those danger, FLV Player by Somoto Ltd can hides deeply in the system and then collect your information without being detected or being influenced,thus your private information and your online activity will be exposed to some one that might use those for malicious purpose, like asking for ransom or threaten you. Besides, FLV Player by Somoto Ltd can open the backdoor in a way that no antivirus could find it and then make your computer more vulnerable to those cyber crackers or cyber criminals. Study recently also showed that it can slower down computer’s performance and can cause freeze sometime. Thus removing it from your computer will be your top priority as long as you find it or it unfortunately being detected.


You may curious wbyAntivirus could not remove it? Because it hides deeply first and second it can disable and end the process of antivirus to better survive. So you should manually remove it.In the following post , I will show you the instruction to remove it and if you have any problem or difficulty, please feel free to contact us here.


Why you need to remove it:

1: FLV Player by Somoto Ltd makes your computer more vulnerable to crackers and virus
2: FLV Player by Somoto Ltd can collect your information.
3: FLV Player by Somoto Ltd can bring other deadly threats to your computer.
4: FLV Player by Somoto Ltd can modify the registry and delete them .

 How to remove it?

Step 1: Enter the safe mode with networking.
Boot up the computer, press F8 at the very beginning and then choose “Safe Mode with Networking”  and press Enter to get in the safe mode with networking.


Step 2: Show the hidden files
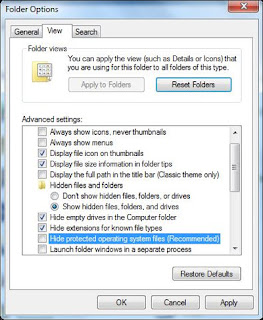
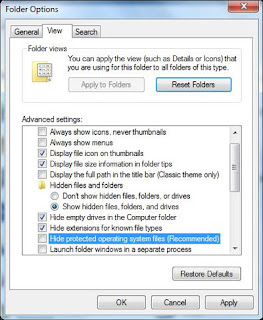
Open Control Panel in Start menu and search for Folder Options. When you’re in Folder Options window, please click on its View tab, check Show hidden files and folders and uncheck Hide protected operating system files (Recommended) and then press OK.


Step 3: Remove it from the control panel.
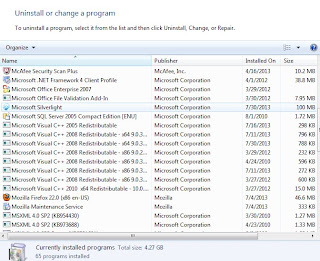
Click starr>>Control Panel>>Program>>Uninstall a Program. FInd the trojan and remove it.


Step 4: Enter the registry editor and delete the corrupted entries.
Tap Windows+R keys together to pop up the Run box, type in regedit and hit OK to open Registry Editor; then find out the following FLV Player by Somoto Ltd  registry entries and delete:


Find the following registered email and delete them.
   HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
  HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
  HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe

If you haven’t sufficient expertise in handling virus program files, processes, dll files and registry entries, you will take the risk of messing up your computer and making it crash down finally. If you need online professional tech support, click here to get:24/7 Online Virus Removal Support.

How to Remove PUP.Optional.Wajam.A


Description of  PUP.Optional.Wajam.A

PUP.Optional.Wajam.A is a notorious Trojan horse that belong s to the group of PUP. Optional family. According to the latest study, we have found that PUP.Optional.Wajam.A also have other members, like PUP.Optional.InstallCore.A, PUM.UserWLoad. This virus can seek every weakness or backdoor on your computer and exploit advanced root kit technology to get on your computer. If your computer is attacked by PUP.Optional.Wajam.A, Your computer will runs more slowly than before and have other weird thing happen because it runs in the backstage and take up certain amount of resources.  First thing that a compromised computer will suffer is that the change of system file and registry, which is the most important part. It can change the system’s setting and delete or modify the registry on your computer, like adding some startup items to the registry which causes system takes time load these items and might cause instability.

Apart from these, PUP.Optional.InstallCore.A can make up some fake security alert which ask you to uninstall some legit programs and it will install other programs in your computer. That’s may explain why your computer is running slower than before. With the help of PUP.Optional.InstallCore.A, crackers sneaks into your computer and the evil things that you can never imagine.. They can watch what you are doing on your computer and then steal your private information for other malicious purposes.  You might want to know why the antivirus failed to completely remove it, and the one reason is that PUP.Optional.Wajam.A can stop some programs or disable them and the other is that it hides deeply in the system file that antivirus mistakes it as legal programs.


How catch it

1: viewing the porn sites.
2: Downloading something from the insecure sites and install it.
3: Clicking  links or attachment form the spam email.


How to remove it

Step 1: Enter the safe mode with networking.
Keep tapping F8 when you launh your computer, and then choose “safe modew tih networking”.


 Step 2: En the process of PUP.Optional.InstallCore.A .
    Hit “Ctrl+Alt+Alt” at the same time to enter the task manager.


Find the random.exe and remove it.

Step 3: Go to  the control panel, find the Trojan and remove it.
    Click Start menu,and then go to Control Panel and, finally choose Uninstall a Program.
                                                                                                                                                                            
Step 4: Enter the registry editor and delete the useless registry entries.
    Press”Win+R” at the same time and then type “regedit” to enter the registry.


Find the following registry entries and delete it.
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random

NOTE:If you have any difficulty removing it, please feel free to contact 24/7 online tech support  at anytime. Your computer will be fine with us.


Monday, September 2, 2013

How to remove Search Donkey Ad

Descripton of Search Donkey Ad

Search Donkey Ad is ad popup that keeps displaying ads in your computer. Once infected with Nym1.ib.adnxs.com, youwill find that you will be interrupted by constant pop-ups and Ads which can lead you to other sites. Recently we have studied its code and find that this malicious pop-ups can also slow down your PC’s performance  and significantly drag down the speed of loading If you are infected with it, you should remove it as soon as possible as it is a real danger. 

Actually, most computers can get infected with Search Donkey Ad, but if you download free soft wares from the other sites, you will be infected with it as Search Donkey Ad is bundled with other programs. Besides, visiting those insecure sites or clicking links in these sites will also increase your possibilities of being infected.

Those compromised computers are easily being control by those who designed this popup because you computer have been infiltrated by it and thus thus it is a matter of time when those evil men begin their next move. This popup ad can open the ports to provide crackers with convenience so that they can access your computer more easily. Besides, this pop up might redirect you to other sites that contain virus. Besides, registry and system setting will be replaced or modified to hide it. But above all, your personal information will be exposed to others, because they will collect your information.


 How to remove it

Step 1: Please enter the Task Manager and end the process.
  Press”Ctrl+Alt+Del” to enter the Task Manager, find Random.exe and end it.


Step 2: disable startup items
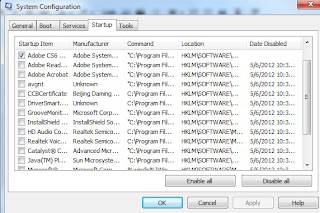
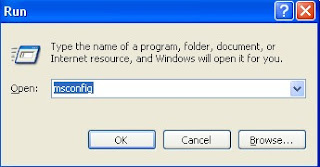
  click Start menu>>type msconfig in the search bar >> open System Configuration Utility >>   Disable all possible startup items generated from  Search Donkey Ad.


Step 3: Enter the registry.
Press”Win+R” and then type ” regedit” in the box and hit “OK”.


Find these registry entries and delete them:
  HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
  HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
  HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe

 NOTE: If you have any problem removing it or couldn't take you off your busy schedule, please go to 24/7 professional online tech support.


How to Remove Trojan Horse Generic32.CEMU

What is   Trojan Horse Generic32.CEMU

Trojan Horse Generic32.CEMU is a stubborn virus that is reported by AVG which can do nothing about it. This virus belongs to the Trojan Horse Generic series that may cause great danger to computers.  Normally, computers connected to the Internet have the same opportunity to be caught by it, but visiting insecure sites, download free programs and click pop ups causally will increase the possibilities of being infected. If your computer unfortunately catches it, you have to remove it as soon as possible because it is the equivalent of Pandora’s Box—it can bring or release many threats to your computer. Here we made a conclusion about Trojan Horse Generic32.CEMU

First, it is a Trojan that can incur other virus, like FBI or ICE Cyber Criminal. We have dealt with some customers and found couple notorious viruses among which are delta search.com, otshot or FBI Money Pak. Second, this virus can open backdoor—ports—to make crackers or cyber criminals easier access to your computer. If they have successfully landed on your computer without being detected by antiviruses, that would be horrible for

Sunday, September 1, 2013

How to Remove PUM.UserWLoad


PUM.UserWLoad is a horrible Trojan that compromises computers in a sneaky way. If you finf PUM.UserWLoad in your computer, you should removed it immediately before it makes damage to your computer. Some users may find that PUM.UserWLoadis very hard to be removed with antivirus. Yes, indeed, because it hides so deeply in the system an mutates at quick speed while antivirus always keeps the same. Besides, if the computer being caught with PUM.UserWLoad,  computer would run weird and may crash down sometimes because this Trojan takes up certain amount and it will change your system setting and registry , ending up with the instability of your computer.

Once it gets on your computer, you may not realize it until the antivirus gives you the warning. You delete it with antivirus but not completely remove it. The rest of it can still function in your computer, carrying out it tasks, like recording your online activity, collecting your private information and change the system setting, delete system files and open the backdoor to provide convenience so that hackers or crackers can easily get in to your system and control your computer.Besides, it can always bring other computer threats like FBI money pak or Trojan Horse Generic33.CDPK or to mess up your computer.

So here you should be more careful. Do not go to those insecure sites or download files from those sites. In addition, you should not open those spam emails and need to delete them once you receive because they always contain a link and most people click it out of curiosity. And one more thing that deserve your attention is do not click any suspicious pop up in your window because these popups,like those links or attachment in the spam Emails ,also contain virus. If you catch it unfortunately, here we provide some useful advices and removal instruction for you.


Removal instruction

If you have any problem removing it, please contact professional online tech support.Ok, here we go.
First: we need to enter the safe mode with networking.
  Keep tapping F8 when you restart your computer and then choose enter the safe mode with networking.


Second: Show the hidden files.
Click  Start>>Control Panel>>Appearance and Personalization>>Folder option, then please click on its View tab, check Show hidden files and folders and uncheck Hide protected operating system files (Recommended) and then press OK.


Third: Enter the registry and delete corrupted registries.
    Press"Win+R" anf then type regedit in he dialog box and hit OK.


Go the following registry and delete any suspicious items.
    HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run
    HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run

Final step: restart your computer to make your change effective.

If you haven’t sufficient PC expertise and don’t want to make things worse, to remove the XY infection safely and permanently, please contact Tee Support PC experts online 24/7 here to clean up the infection in a few minutes without repeating.