Tuesday, September 10, 2013

Infected with PC Power speed. Removal Instruction.

What is PC Power Speed

PC Power Speed is a fake antivirus that pretends to be a legitimate program and gets on your computer without your permission. It can be distributed by spam Emails, pop ups from the websites or bundle with third party program. Once your compute is infected with this virus, it will scan your computer and then report a lot of problems. And then PC Power Speed will ask you to pay for its full edition.  If you choose to pay for it, well, a financial loss is inevitable.

 When it scan your computer, do not think that it is doing its legal job. It can scan your system’s vulnerability, open ports, peek at your files. Once it learns your system’s weakness, it will fully exploit it and implant Trojan horses in your computer by opening ports. It can also copy all your files or walk away those files that consider important. After finishing scanning, it will report a lot of infections and urge you to pay for full edition. This is their common tricks.

How to Remove PUP.Optional.OpenCandy

What is PUP.Optional.OpenCandy

PUP.Optional.OpenCandy can be categorized as a Trojan that can infect computers and cause great damage to the compromised computer. It belongs to the PUP. Optional group and is the most notorious one as its devastating power. There are also other  PUP.Optional.members, like PUP.Optional.Wajam.A, PUM.UserWLoad, PUP.Optional.InstallCore.A.  This virus uses advanced rootkit technology  and can delicate itself  in your computer to increase its chances of staying in your computer. By seeking the weakness of your computer and taking advantage of it, PUP.Optional.OpenCandy can easily gets on your computer and conduct evil things in your computer.

 Potential threats

First, it can find your files, copy all files and transfer to someone. In this case, your information will be exposed to the public and others could use it for evil purposes. Second, computer’s performance is not so satisfying than before because PUP.Optional.OpenCandy needs to run and transfer information during which will take up certain amount of resources. Third is that PUP.Optional.OpenCandy can add some harmful to the registry, like startup entries. This is the most dangerous part because, as we

Monday, September 9, 2013

How to Remove PUP.Optional.Conduit.A

What is PUP.Optional.Conduit.A

PUP.Optional.Conduit.A is a harmful computer threat that can infiltrate your computer
and do many things that totally beyond your imagination. This Trojan can be
distributed by spam e-mails in which it is disguised as an attachment or a link,
third-party programs that bundles with them and popups appeared when you visiting
those unsecure sites. Once you click those links or pop-ups or open those
attachments, then PUP.Optional.Conduit.A can get on your computer in a way that,
sometimes, antivirus fails to detect its infiltration.

It is just like opening a Pandora’s Box once a computer is infected with PUP.Optional.Conduit.A because its potential power to devastate your computer. First it can block you to run some programs to remove it. That could explain why antivirus fails to detect or detect it but could not remove it. Second, it can bring so many threats to compromise your browser, system or files. For example, we have dealt cases in which their IE was completely infected and every time users try to download something, a warning pops up and said” this file contain a virus and was delete”; Or their

How to Remove CryptoLocker

What is CryptoLocker 
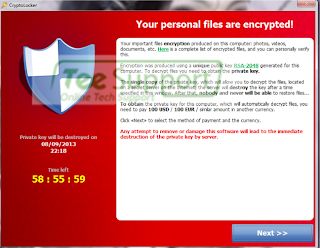
CryptoLocker now is a ransomware that prevailing in the North America. Any computer infected with this is virus will be locked and receive a large warning, saying in order to obtain the private key, you have to pay 100 dollar or 100 euro for this. CryptoLocker also warns you that if you attempt to remove it, it will destruct the private key. You should not believe such a scam as there are too many of such viruses or ransomware that has been gained much notoriety, like ICE Cyber Crimes Center Virus, Cheshire Police Authority Ukash and Homeland Security Virus.

Saturday, September 7, 2013

How to Remove Safe Monitor

What is Safe Mode

Safe Monitor is a useless add-on that gets on computers without permission. It is created by those cyber criminals who are driven by profits. The way to gain profit for Safe Monitor is to keep displaying ads, pop-ups and links on your computer and if you click them, it will redirect you to certain websites that consider harboring tongs of viruses. And then something weird begins to show up.

First, you will find you browsing are severely influenced by continuous pop-ups, because this is its main purpose. Second, Safe Monitor can not only install itself on your computer, but also incur other threats to your computer,like ICE, otshot. Third, you will find computer’s performance is sliced down significantly. But the most important thing is its ability to open the backdoor to the crackers and let them access your computer and monitor what you do on your computer. This sounds impossible but it did happen before, and someone had lost his account and his most important information as crackers successfully infiltrated their computers. Here we list several reasons about why you need you remove it as soon as possible.

Manually Remove Jvl.libpack.net


what is  http://jvl.libpack.net
Jvl.libpack.net is a browser hijacker that could reroute your Google Chrome, firefox or other browser or search engine to the http://jvl.libpack.net. It can be distribute by various ways, like spam e-mails in which it is disguised as a link or attachment, pop ups at the corner of the desktop ,free downloads like movies, executive files and third party programs which are bundled with http://jvl.libpack.net. 

When a computer is compromised by http://jvl.libpack.net, homepage and search engine which are the first victims, will be replaced by http://jvl.libpack.net. So whatever you are trying to search on the search bar, you will be redirected to http://jvl.libpack.net or other totally irrelevant sites. Then it can collect your searching queries or searching key word so that it can display the proper ads or pop-ups in you r computer to promote its ad revenue.  Apart from those threats, it can also slow down the performance of you r computer  and the browser takes long time to load a page ,sometimes even failed to load because this browser hijacker takes up certain amount of resource to run it and sending message to remote server. Bu the the last threats we try to highlight is that its ability to modify registry. It can add some registry entries to the registry to make it become default search engine or homepage. We should know that any amendment to the registry should be made with consideration. Any casual modifying can only do harm to the stability of your computer. So we have to remove it as long as it is spotted.

 Removal Instruction

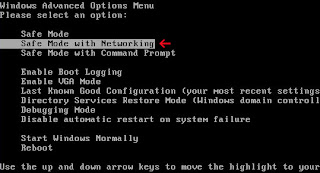
Step 1: Enter the Safe Mode with Networking.
Keep tapping F8 when you restart your computer and then choose Safe Mode with Networking.


Step 2: Open the Task Manager and end the process.
Hit Ctrl+Alt+Del to enter the Task Manager.


Find Random.exe and end it.

Step 3: Got to the registry, find corrupted entries and delete them all.
Press”Win+R”>>Type”regedit”and hit OK


Find the following corrupted entries and remove it
  HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
  HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
  HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe

Step 4: Restart the computer to make the change effective.

Manual removal could help you completely remove it, but it requires users with basic training in computer. If you could not remove it on your own, please feel free to contact our professional help from 24/7 online tech support.


Friday, September 6, 2013

How to Remove cloud-connect.net - Manual Removal Help


What is cloud-connect.net

Cloud-connect.net is a browser hijacker that could change your browser setting and redirect you to cloud-connect.net, cloud-connect.com,etc.  You can pick it up anywhere if you do not have a good browsing habit, like viewing insecure sites as porn sites. It can also be bundled with other problems and you will increase your possibility of being caught by it if you choose quicker way or default way to install a program.


Infecting with cloud-connect.net is quite annoying because it keeps redirecting you to other sites. Whatever you search in the searching box, you will be redirect malicious websites that contain viruses because you homepage and default engine were replaced by cloud-connect.net. It can also install toolbars in your computer and collect your searching queries so that it can display relevant commercials, pop ups or links. Although tiny it is, cloud-connect.net has shown us how hard it is to remove it. Some of our clients told us that they spent couples hours to remove it but no results turned out and they were going to freak out. Cloud-connect.net can drag down computer performance and take up broadband, that’s may explain that why page loading speed is sliced down significantly or sometimes computer freeze there.

 Here are some typical symptoms that will occur when your computer unfortunately catches cloud-connect.net:

1: Your homepage and default engine is changed.
2: A lot of pop-ups, commercials are displayed when browsing the Internet.
3: Computer’s performance sliced down, sometimes freezing or blue screen will take place.
4: You are always redirected to other sites.
To crown the whole, registry is changed and thus making your computer more vulnerable to the attack from the virus. SO removing it now.

Removal Instruction:

Step 1: launch your computer into Safe Mode with Networking.
  Restart your computer>> keep tapping F8 when the compute restarts>>Choose Safe Mode with Networking.


Step 2: Disable any suspicious startup items that are made by infections from this virus.
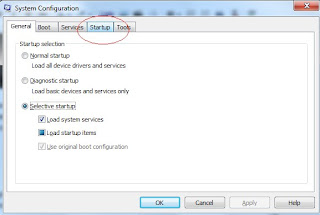
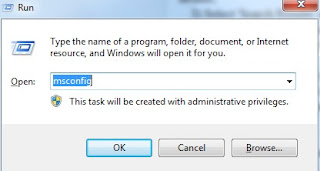
  Press”Win+R”>>type “msconfig” and hit OK>>click tab “Startup”>> Disable all possible startup items generated from cloud-connect.net.


Step 3: Remove Add-ons
  Internet Explorer
    1) Go to 'Tools' → 'Manage Add-ons';
    2) Choose 'Search Providers' → choose 'Bing' search engine or 'Google' search engine and make it default;
    3) Select 'Search Results' and click 'Remove' to remove it;
    4)  Go to 'Tools' → 'Internet Options', select 'General tab' and click 'Use default' button or enter your own website, e.g. Google.com. Click OK to save the changes.
  Mozilla Firefox
    1) Click on the magnifier's icon and select 'Manage Search Engines....';
    2) Choose 'Search Results' from the list and click 'Remove' and OK to save changes;
    3) Go to 'Tools' → 'Options'. Reset the startup homepage or change it to google.com under the   'General tab';
  Google Chrome
    1) Click on 'Customize and control' Google Chrome icon, select 'Settings';
    2) Choose 'Basic Options'.
    3) Change Google Chrome's homepage to google.com or any other and click the 'Manage search engines...' button;
    4) Select 'Google' from the list and make it your default search engine;
    5) Select 'Search Results' from the list remove it by clicking the "X" mark.

Step 4: Open the registry entries.
  Hit “Win+R” and then type “regedit”.


Find the following entries and remove them:
  HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
  HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ‘Random’
  HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
  HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
  HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe


Step 5: Reboot the system.

Manaul removal might require certain education in computer. If you are not so sure you can remove it totally, please feel free to contact us at anytime available.