Monday, October 21, 2013

How to Remove big.deluxeforthefuture.com Redirect

What is ig.deluxeforthefuture.com


Big.deluxeforthefuture.com Redirect  is a browser hijacker that could get on your computer without your permission and then replace your browser homepage and continue to do harm to your machine. Big.deluxeforthefuture.com usually packs with Spam mails or disguise it as innocent attachments. Also, if you have ever visited those insecure sites, then you have great chance of being infected. The last and most common way is that it could be bundled with other programs and when you install the in the typical way, that would put your computer in a dangerous situation.


Computers which were infected with big.deluxeforthefuture.com will become weird. First users may find that their homepages are replaced with big.deluxeforthefuture.com. Every time when they open the browser or

Saturday, October 19, 2013

How to Remvoe Http://gzj.jsopen.net

Http://gzj.jsopen.net is a browser hijacker viruses that get itself installed in the compromised computers without users’ permission. This is a nasty and stubborn browser hijacker that could be  distributed by spam emails as links that attached in the emails, but a more common way is that users click the pop-ups in the insecure sites or download the free software from those sites and install the in the typical way.It is proved that this malicious virus can hijack browsers including Internet Explorer, Mozilla Firefox, Google Chrome etc. If it is installed in the computer, it can modify browser settings to redirect user to other malicious websites that contain virus, Trojans, malwares or other threats that could pose a great risk to those compromised computers.

At the very beginning, you will find that every time you go to the search bar on the Google, IE or Firefox Mozilla to search up something, it lags and then when you click search results, you are kept redirecting to a different site. In addition to changing your homepage, it can also change your default search engine such as Google, Yahoo and Bing to other search engine. Obviously, this is a bogus search engine. No matter what you want to search on the browser, you will be presented a lot of unwanted information.besides, it can bring like sweetpack 3.0 to your PC so that those hacker criminals can conllect your online activities and store all your personal and financial data you enter on different pages, like your Facebook account. In that case, you have no privacy and face a great risk of losing your precious data. Therefore, never look down upon Http://gzj.jsopen.net, it can bring huge risk to your PC. Once detected, you should immediately get rid of Http://gzj.jsopen.net virus as soon as possible.


Removal guide:


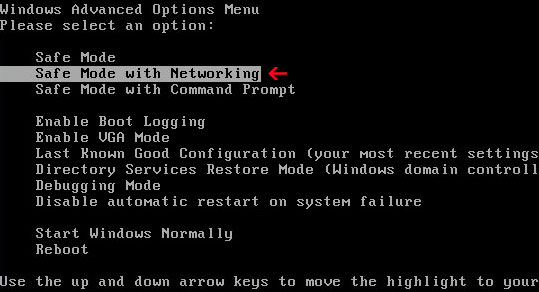
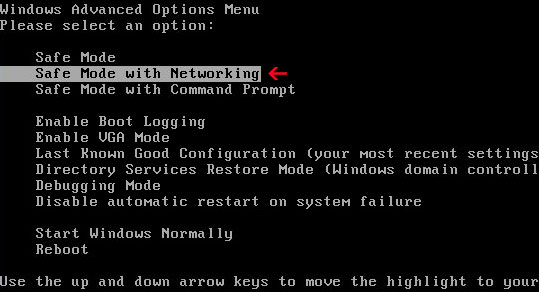
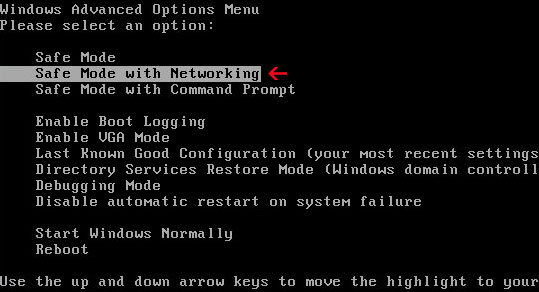
Step 1: enter the safe mode with networking.
1: restart your computer
2: keep tapping F8 when the computer restarts but before windows launches
3: Use the arrow keys to highlight the “Safe Mode with Networking” option and then press Enter


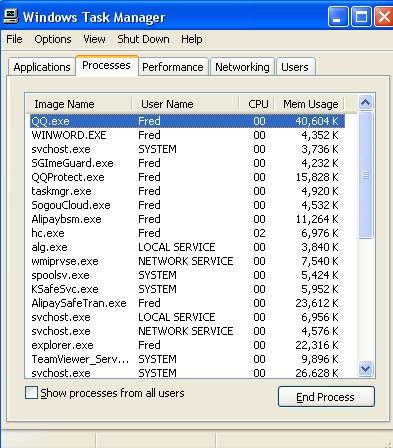
Step 2: Enter the Task Manager and end related tasks.
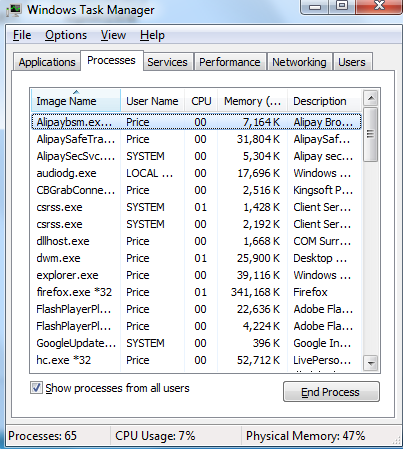
press CTRL+ALT+DEL to enter the Task Manager,click Random.exe and end them.


Step 3: remove the program from control panel.
1>. Find the “start” button on the lower left corner of your monitor, and then click it.
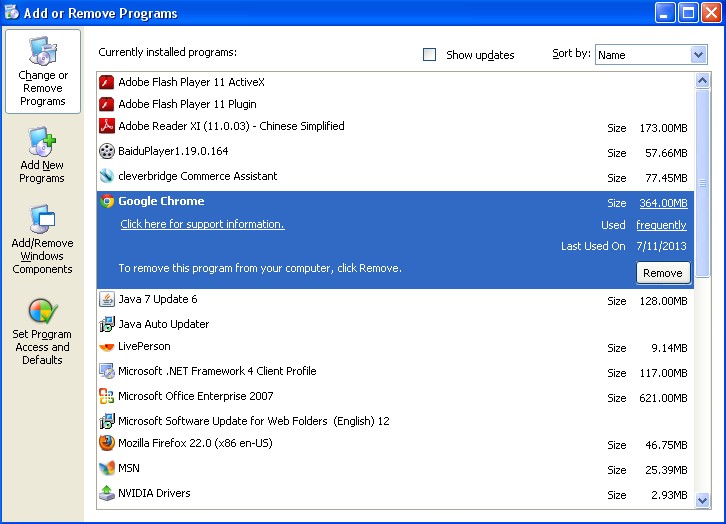
2>. Find and double click the button “Control Panel” and then choose "Uninstall a Program".
3>. When the windows pop up, find Http://gzj.jsopen.net icon in the list, and then select it to start uninstalling it from your computer by clicking “Uninstall”.


Step 4: When it is finished, reboot your computer to take effect.

Note: Manual Removal requires expertise and it is for advanced users, if you don’t have much experience in dealing with redirect virus. Contact Tee Support agents 24/7 online Service.

How to Remove A2ZLyrics.A

What is A2ZLyrics.A

A2ZLyrics.A is an unwanted program that hijacks your computer and try to mess it up from  the day it gets into the target browser. Although some people  may consider it a harmless program that they think it is unnecessary to remove it, but the fact is that A2ZLyrics.A can be a truly unnerving thing on your daily activities. Some users may wonder how this adware get itself rooted in the target system, there are some ways it use such as pretending as a tempting ads or an innocent email attachment is always succeed with users’ inattention. If users go to those insecure sites or download free things free the Internet or install a program that choose the typical way to install it, it bear the same opportunity of being infected with What is A2ZLyrics.A. Base on that, this adware has successfully taken charge of the victim browser and bring in other threats.

Some add-on or piece of codes to plug-in can be added to target browser such as Mozilla Firefox, Internet Explorer or Google Chrome. With the help of the plug-ins, this hijacker can replace original settings of DNS, homepage and search engine to the one in its favor. Then it will keep redirecting you to the insecure sites or other irrelevant sites and your search result will be recorded so that it can pop up relevant ads or links that you are or you may interest in. It will also slow down your whole computer by loading numerous advertising pop-ups; stop security programs from detecting or removal. But the most worried thing is that A2ZLyrics.A can open your backdoor so that hacker can easily gain the access to your computer and copy your files and other important information. So PC users must have it removed before the computer crash and have no use at all.


How to remove A2ZLyrics.A?


Step 1: Launch your computer into the Safe Mode with Networking.
Keep tapping F8 when you launch your computer, and then choose Safe Mode with Networking.


Step 2: En the process of PUP.Optional.A2ZLyrics.A.
Hit Ctrl+Alt+Alt to enter the task manager.

Find the Random.exe and end it.

Step 3: Go to the control panel, find the Trojan and remove it.
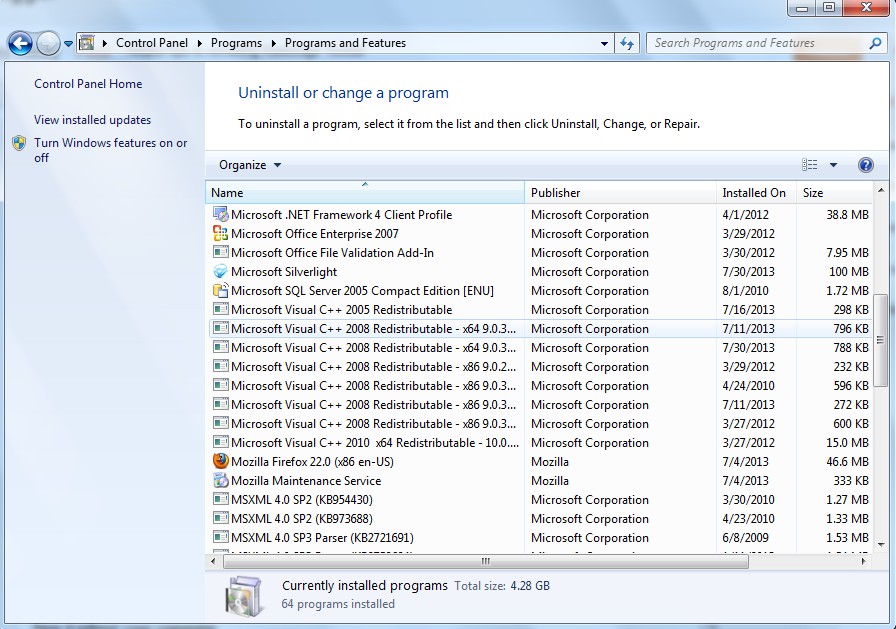
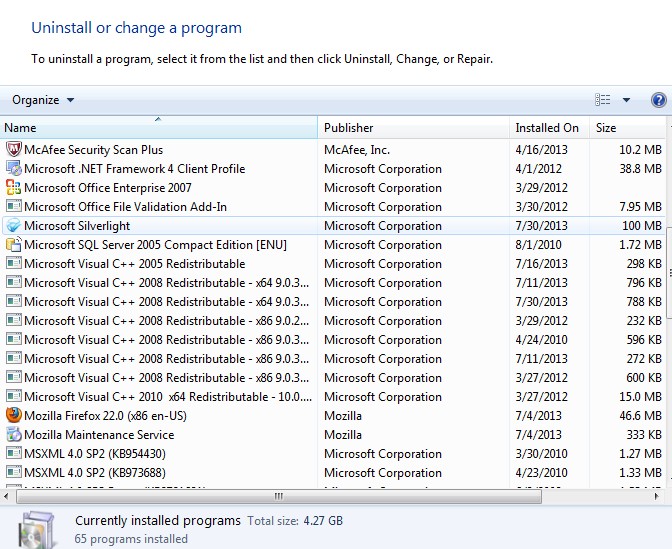
Click Start menu,and then go to Control Panel and, finally choose Uninstall a Program.

                          
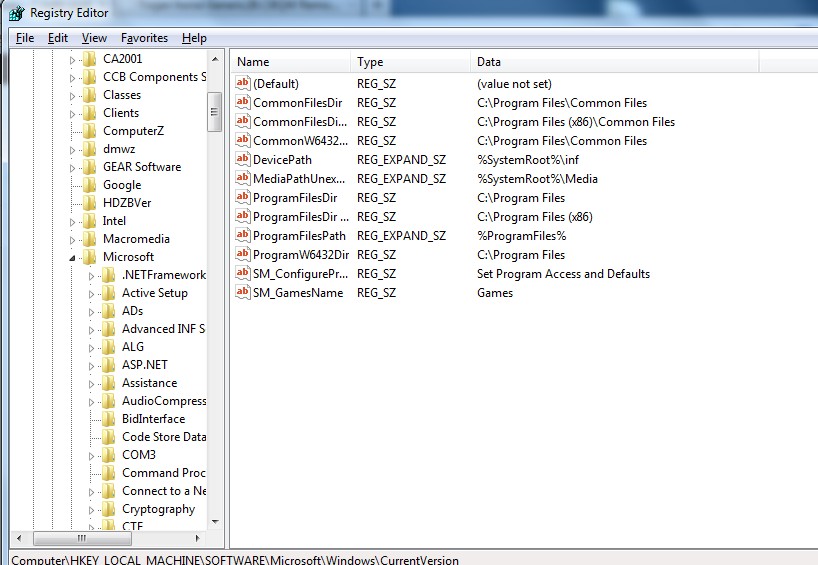
 Step 4: Go to the registry editor and delete the useless registry entries.
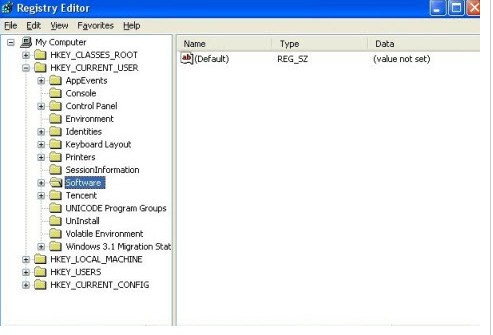
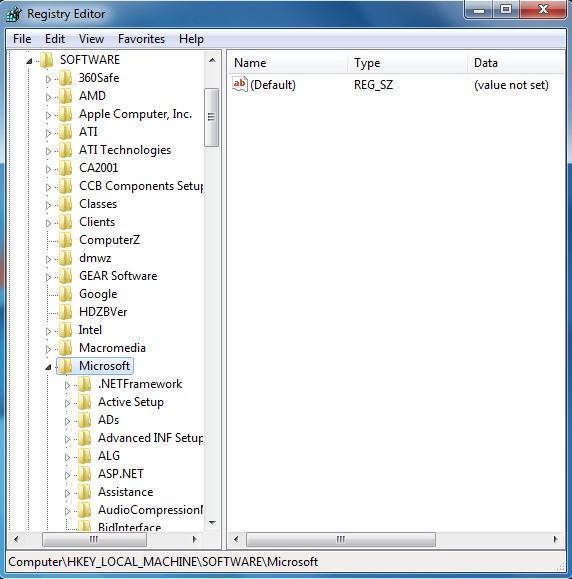
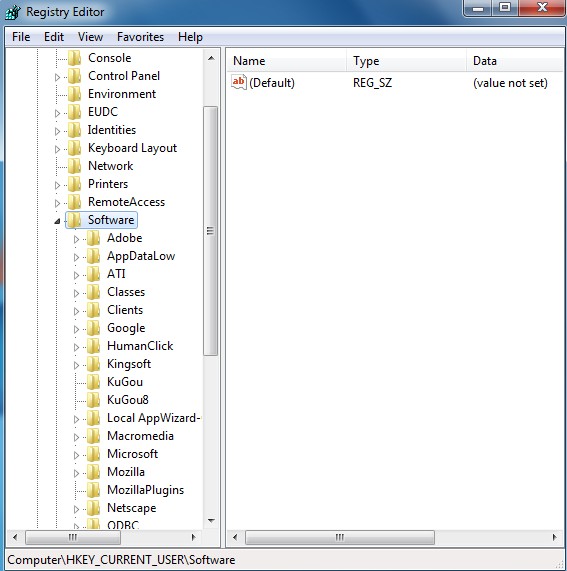
 Press Win+R and then type regedit to enter the registry.

Find the following registry entries and then remove them:
KEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ‘Random’
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe

It is impossible to list all file names or locations of the tracksrv.com here. You can check the remaining parasites, leftover files or get instant help by getting online tech support 24/7 here.


Friday, October 18, 2013

How to Remove Hitfollower.info

What is Hitfollower.info? Every time when you try to search for something, it keeps popping up and when I click the search results, it just leads me to Hitfollower.info. How can I get rid of it? What did I get infected with this annoying thing?

What is Hitfollower.info?


Hitfollower.info is a browser hijacker that intends to get you to its website for malicious purposes. It can change your home page and your default search engine, result in leading you to its page when you clink any link on your browser, collecting your private information even displaying advertisements and etc. When you open a new tab, you will be redirected to Hitfollower.info.  Your search box is infected and if you type query words in search box, all the search results are attached with Hitfollower.info domain instead of Google or Yahoo and  redirect to its page. Besides, it will pop up automatically when you browse the page.

How Do I Get Infected?


Many user don’t know how they get infected so they next time will learn how to prevent it .Many would say “oh, I didn’t download it” , ” how could I get  such annoying thing in my computer? Nope. Actually, it is themselves ,the users, who download this virus and install it ,but who shouldn’t be to blame, because this tricky thing can slip into  your computer when you view the insecure page, thus get infected or installed a free software that have bundled into the installation before you realize and even your antivirus can detect that.

Damage that comes Along with Hitfollower.info


1: Home page is replaced with Duckduckgo.com and all your search results are redirected to it.
2: Default search engine is changed to Hitfollower.info.
3: Display advertisements and sponsored links in your search results
4: Collect search terms from your search queries and get some information about you.
5: Hook deep into your operating system and make preparation for further attack or invasion.

How to Remove It?


Step 1: Open your task manager and terminate related process.
Press Ctrl+Alt+Del and choose Start Task Manager and click Processes. Find related Find Random.exe, click it and then click End Processes.


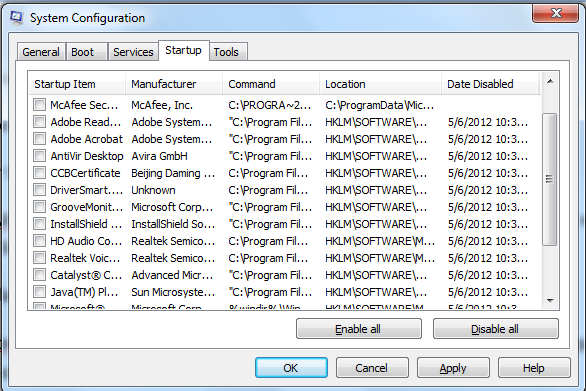
Step2: Disable any suspicious startup items.
Click Start menu -> click Run -> type: msconfig in the search bar -> open System Configuration Utility -> Disable all possible startup items including those of Duckduckgo.com:


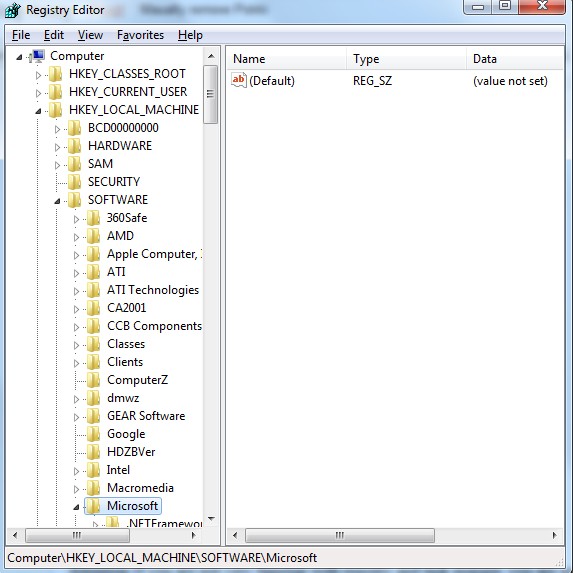
Step 3: Delete related registry values.
Press  Win+R at the same time, then enter regedit in the dialogue box and hit Enter to access to the registry editor.


Find and delete following related registry value:

HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run ‘Random’HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “Certification” =Random

NOTE: If you haven’t sufficient expertise in dealing with program files, processes, DLL files and registry entries, it is not recommended to delete by yourself. Because any pivotal system files are removed, you cannot log in Windows at all. Click here and get help from Tee Support agents 24/7 online Service.


Thursday, October 17, 2013

How to Remove Trojan.Gen.3

Description of  Trojan.Gen.3 


 Trojan.Gen.3 is a notorious Trojan horse that could crash down your computer. According to the latest study, we have found that  Trojan.Gen.3 also have other members, like PUP.Optional.InstallCore.A, PUM.UserWLoad. This virus can scan every vulnerability or backdoor on your computer and exploit advanced rootkit technology to get on your computer. If your computer is attacked by Trojan.Gen.3, Your computer will runs more slowly than before and some other weird thing happen because it runs in the backstage and take up certain amount of resources.  First thing that a compromised computer will suffer is that the change of system file and registry, which is the most important part. Trojan.Gen.3 can change the system’s setting and delete or modify the registry values on your computer, like adding some startup items to the registry which causes system takes time load these items and might cause instability.


Apart from these, PUP.Optional.InstallCore.A can make up some fake security alert which ask you to uninstall some legit programs and it will install other programs in your computer. That’s may explain why your computer is running slower than before. With the help of PUP.Optional.InstallCore.A, crackers sneaks into your computer and the evil things that you can never imagine.. They can watch what you are doing on your computer and then steal your private information for other malicious purposes.  You might want to know why the antivirus failed to completely remove it, and the one reason is that PUP.Optional.Wajam.A can stop some programs or disable them and the other is that it hides deeply in the system file that antivirus mistakes it as legal programs.

How Would I Catch It?


1: viewing the porn sites.
2: Downloading something from the insecure sites and install it.
3: Clicking  links or attachment form the spam email.


How to Remove it


Step 1: Enter the Safe Mode with Networking.
Keep tapping F8 when you launch your computer, and then choose Safe Mode with Networking..


Step 2: End the process of Trojan.Gen.3.
Hit Ctrl+Alt+Alt at the same time to enter the task manager.


Find the random.exe and remove it.

Step 3: Go to  the control panel, find the Trojan and remove it.
Click Start menu,and then go to Control Panel and, finally choose Uninstall a Program.

                                                                                                                                                                Step 4: Enter the registry editor and delete the useless registry entries.
 Press Win+R at the same time and then type regedit to enter the registry.


Find the following registry entries and delete them.
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\CurrentVersion\Random
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random

NOTE:If you have any difficulty removing it, please feel free to contact 24/7 online tech support  at anytime. Your computer will be fine with us.


What is PC Wmdefender.exe

Wmdefender.exe is a fake antivirus that pretends to be a legit program and gets on your computer without your permission.Wmdefender.exe can be a big threat to a computer. It can be distributed by spam Emails, pop ups from the websites or bundle with third party program. Once your compute is infected with this virus, it can give a whole scan on your computer and then report a lot of problems. And then Wmdefender.exe will ask you to pay for its full edition if you want all those problems go forever(of course those problems are made up).If you choose to pay for it, well, a financial loss is inevitable.


When it scans your computer, you should not think that it is doing its legal job. It can scan your system’s weakness and exploit them, open backdoors and get your important files. Once it has learned the whole system configuration, then  it will fully use it and implant Trojan horses in your computer with the help of Wmdefender.exe. It can also steal your files and use them for malicious purpose. We have dealt a customers whose files about M&A with another company had been stolen and thus causing great financial loss to the company. After finishing scanning, it will report a lot of infections and urge you to pay for full edition. This is their common tricks.

If you do not remove it, it can make more damage to your computer or mess up your computer. But how dangerous is it? What threats could it bring in?  First, your antivirus is compromised by this virus and any attempt to run a program to remove it is foiled by Wmdefender.exe, thus makeing your computer vulnerable to other viruses or Trojan horses. Second, it uses a fake warning to scare you and keep popping up that warning which is annoying with it. Third, computer’s performance is significantly dragged down, because this virus takes up more main memory when running a scan  and makes your computer freeze a lot. But the most important is that this virus could make a big change to your registry to make it more legal and to block antivirus process. Therefore,you cannot resort to other antiviruses but have to remove it manually. Wmdefender.exe can also incur other threats to your computer that could totally turn your computer into a virus wonderland.


How to Remove it?


Step 1: Launch your computer into the safe mode with networking.
Keep tapping F8 when your computer restart and then choose Safe Mode with Networking.


Step 2: Go to the Control Panel and remove it
Click Start->Control Panel->Program->Uninstall a program. Find the program and then uninstall it.


Step 3: Go to the registry and delete those corrupted registry values.
 Hit Win+R->type regedit and hit Enter.


Find following entries and remove all of them:
HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun “[rnd].exe”
HKEY_LOCAL_MACHINESOFTWAREMicrosoftWindowsCurrentVersionRun “[rnd].exe”

Find those useless files and delete them all:
 %AllUsersProfile%  random.exe
 %Temp/appdata%  random.exe

NOTE:it is impossible to list all file names or locations of the Wmdefender.exe here. You can check the remaining parasites, leftover files or get instant help by getting online tech support 24/7 here.


Wednesday, October 16, 2013

How to Remove 4shared.com Community Toolbar

 Description of 4shared.com Community Toolbar?


4shared.com Community is a toolbar that get installed in your computer without your permission. It is a dangerous toolbar to the computer as its designers try to use it to get into your computer. Basically, 4shared.com Community Toolbar usually packs with Spam mails or disguise it as innocent attachments. When people click it out of curiosity, they computer will get infected with this nasty virus. Second, some insecure sites may contain virus and you will easily get infected with if you visit them. The last and most common way for this virus to spread is by bundling with other programs and if you choose to install it by the typical way instead of custom way, then there are much great possibility of being infected with this virus.


When a computer infected with 4shared.com Community Toolbar, its browser homepage might be changed and replaced with other home page and system setting is also changed in order to better reside in a compromised computer. Besides, 4shared.com Community Toolbar also add corrupted registry to the start-up items so that every time when you start your computer, it will be launched. But those redundant registry values are unnecessary to the computer and thus will give birth to the slowdown of your computer. During its running, tons of junk files will be created. They not only take up certain amount of resource, but also occupy the hardware. To top those all is that 4shared.com Community Toolbar can provide convenience to hackers and make gain the access to your computer without much effort.


Some antivirus could not report this virus because it is considered a legal part of the browser. There are many toolbars in the computer and lacking of one of will lead to the failure of some functions. That’s why the antivirus could not report. But when the antivirus did report that, it had already damaged the computer. So it is very pressing to remove it before it makes more damage to the computer.


How to Remove it?


Step -1:  Restart your computer in to the Safe Mode with Networking.


Step-2: Remove it from the browser.
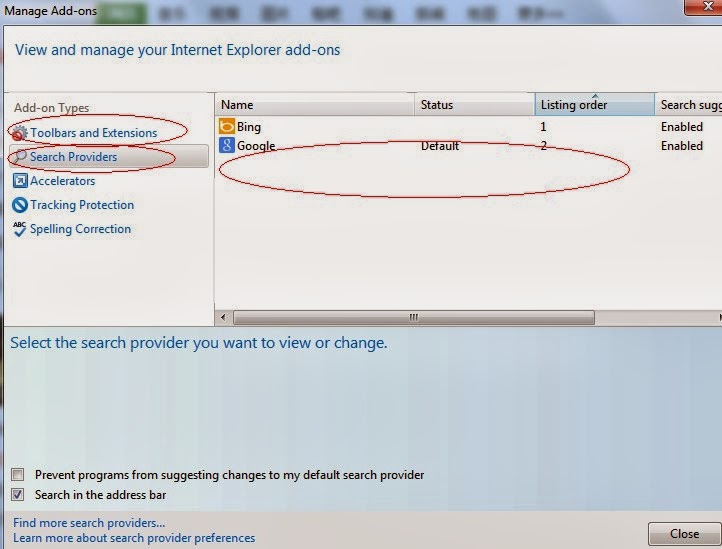
1) Go to 'Tools' → 'Manage Add-ons';
2) Choose 'Search Providers' → choose 'Bing' search engine or 'Google' search engine and make it default;
3) Select 'Search Results' and click 'Remove' to remove it;
4)  Go to 'Tools' → 'Internet Options', select 'General tab' and click 'Use default' button or enter your own website, e.g. Google.com. Click OK to save the changes.


Step-3: Go to the registry editor and then remove corrupted and redundant registry values.
Hit Win+R and then type regedit and hit Enter finally.


Find the following registry values and then delete them all:
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe

Step-4: Restart your computer to make your change effective.

NOTE: If you have anything that you do not understand, please feel free to contact Tee Support 24/7 online tech support. Your computer will be taken good care of.